- IonQ estimates Bitcoin could face a quantum attack using 19,397 physical qubits and 1,457 logical qubits.
- The modeled attack would take 25.7 days per attempt and would not guarantee that a key is recovered.
- IonQ calculated a 40.7% success rate per attempt, while optimistic assumptions raise it to about 63.3%.
Bitcoin’s cryptographic security has received a specific quantum computing threat estimate from IonQ, which puts the required computing power at 19,397 physical qubits.
The company’s study estimates that a fault-tolerant quantum computer with those resources would take 25.7 days to run an attack against Bitcoin’s secp256k1 elliptic curve, although one attempt would not guarantee success.
The research provides a more specific measurement of the Bitcoin quantum threat than broad estimates that focus mainly on the theoretical capabilities of quantum computers.
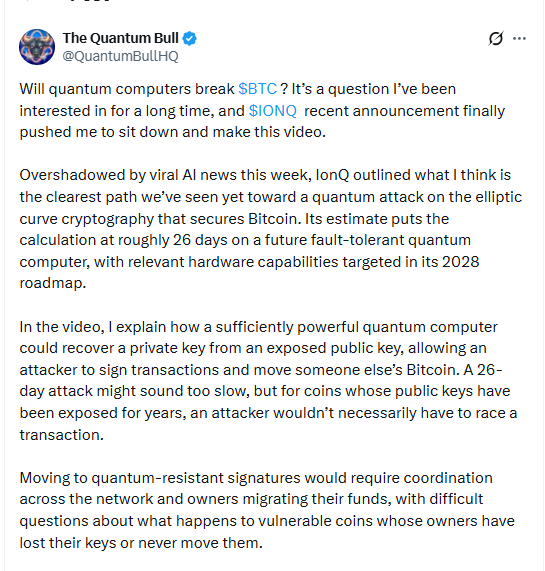
Source: Quantam Bull
IonQ said its analysis accounts for the error-correction processes that a practical machine would need to perform during the attack.
The modeled system would contain 1,457 logical qubits, which are qubits protected against errors through quantum error correction. It would also require approximately 39 million Toffoli logic gates to execute the attack.
How the Bitcoin Quantum Threat Was Calculated
IonQ based its calculations on the Walking Cat architecture, which it published in April 2026 as a full-stack blueprint for a fault-tolerant quantum computer. Researchers then applied that architecture to an attack using Shor’s algorithm against secp256k1, the elliptic curve used by Bitcoin.
The study is designed to account for the resources required across the complete computational process rather than relying only on estimates for the algorithm itself. That distinction matters because error correction represents a significant part of the resources required for a practical fault-tolerant quantum system.
Under IonQ’s model, the resulting machine would require 19,397 physical qubits to support 1,457 logical qubits. The calculation also sets the computational workload at 39 million Toffoli gates.
The estimated runtime is 25.7 consecutive days for one attack attempt. That figure describes the time required for the modeled computation and does not mean an attacker would necessarily obtain a private key after that period.
IonQ calculated a 40.7% lower-bound probability of success for a single attempt. Under more optimistic mathematical assumptions, the success rate could reach approximately 63.3%.
What the Quantum Attack Means for Bitcoin
Bitcoin is based on the use of public and private key pairs. The spending control capability of the key lies within the private key while the security of the system is determined by the level of difficulty of deducing the private key from the public key.
The Bitcoin quantum threat arises from the potential use of Shor’s algorithm on a sufficiently capable quantum computer. The algorithm could change the computational assumptions underlying elliptic curve cryptography, creating a potential route toward deriving private keys from public information.
IonQ’s study does not indicate that such an attack is currently possible. The machine described in the research does not exist today, and the modeled computation remains an engineering requirement rather than an active attack against Bitcoin.
The probability figures also mean that a single 25.7-day run would not necessarily be sufficient. With a 40.7% lower-bound success rate, an unsuccessful attempt could require another run, potentially extending the total time needed to obtain a key.
That distinction is important when interpreting the Bitcoin quantum threat. The research provides a concrete resource estimate for a hypothetical fault-tolerant quantum machine rather than evidence that Bitcoin’s existing cryptography can currently be broken.
IonQ Puts a Specific Scale on the Threat
The significance of the research is the level of detail attached to the estimate. Instead of describing quantum attacks on Bitcoin only in terms of future computational power, IonQ mapped the requirements to a specific architecture and included physical qubits, logical qubits, gate count, runtime, and success probability.
The estimate therefore provides several measurements for evaluating the potential attack rather than relying on a single qubit figure. The 19,397 physical-qubit requirement is the headline number, but the 1,457 logical qubits and 39 million Toffoli gates define additional parts of the modeled workload.
For Bitcoin, the study places the quantum-security question in measurable engineering terms. However, the figures remain tied to IonQ’s modeled architecture and assumptions, and the absence of a machine capable of executing the attack means the Bitcoin quantum threat remains a future technical concern based on the supplied research.
FAQs
How many qubits would IonQ’s model require to attack Bitcoin?
The company believes that the model of the fault-tolerant quantum computer would need 19,397 physical qubits and 1,457 logical qubits.
How long would one Bitcoin quantum attack take?
The study estimates 25.7 days of continuous computation for a single attack attempt.
Would one 25.7-day attack guarantee success?
No. IonQ calculated a 40.7% lower-bound success probability per attempt and about 63.3% under more optimistic mathematical assumptions.